
Secure Email Agentic Manager
Manage, analyze, and govern DMARC data with an intelligent agent integrated into the Microsoft ecosystem.
THE APPLICATION CONTEXT
Email authentication, visibility, and spoofing risk
Email authentication is a fundamental element in protecting business domains from spam, phishing, spoofing, and domain abuse. The main protocols are SPF, DKIM and DMARC: SPF defines which servers are authorized to send emails on behalf of a domain, DKIM adds a digital signature to verify authenticity and integrity, while DMARC relies on SPF and DKIM to define policies for handling non-compliant messages and generating reports to the domain owner. However, adopting DMARC is not limited to publishing a DNS record. To be truly effective, it requires collecting reports, continuous analysis, identifying misconfigurations, managing subdomains, and a gradual shift towards more restrictive policies such as quarantine and reject.
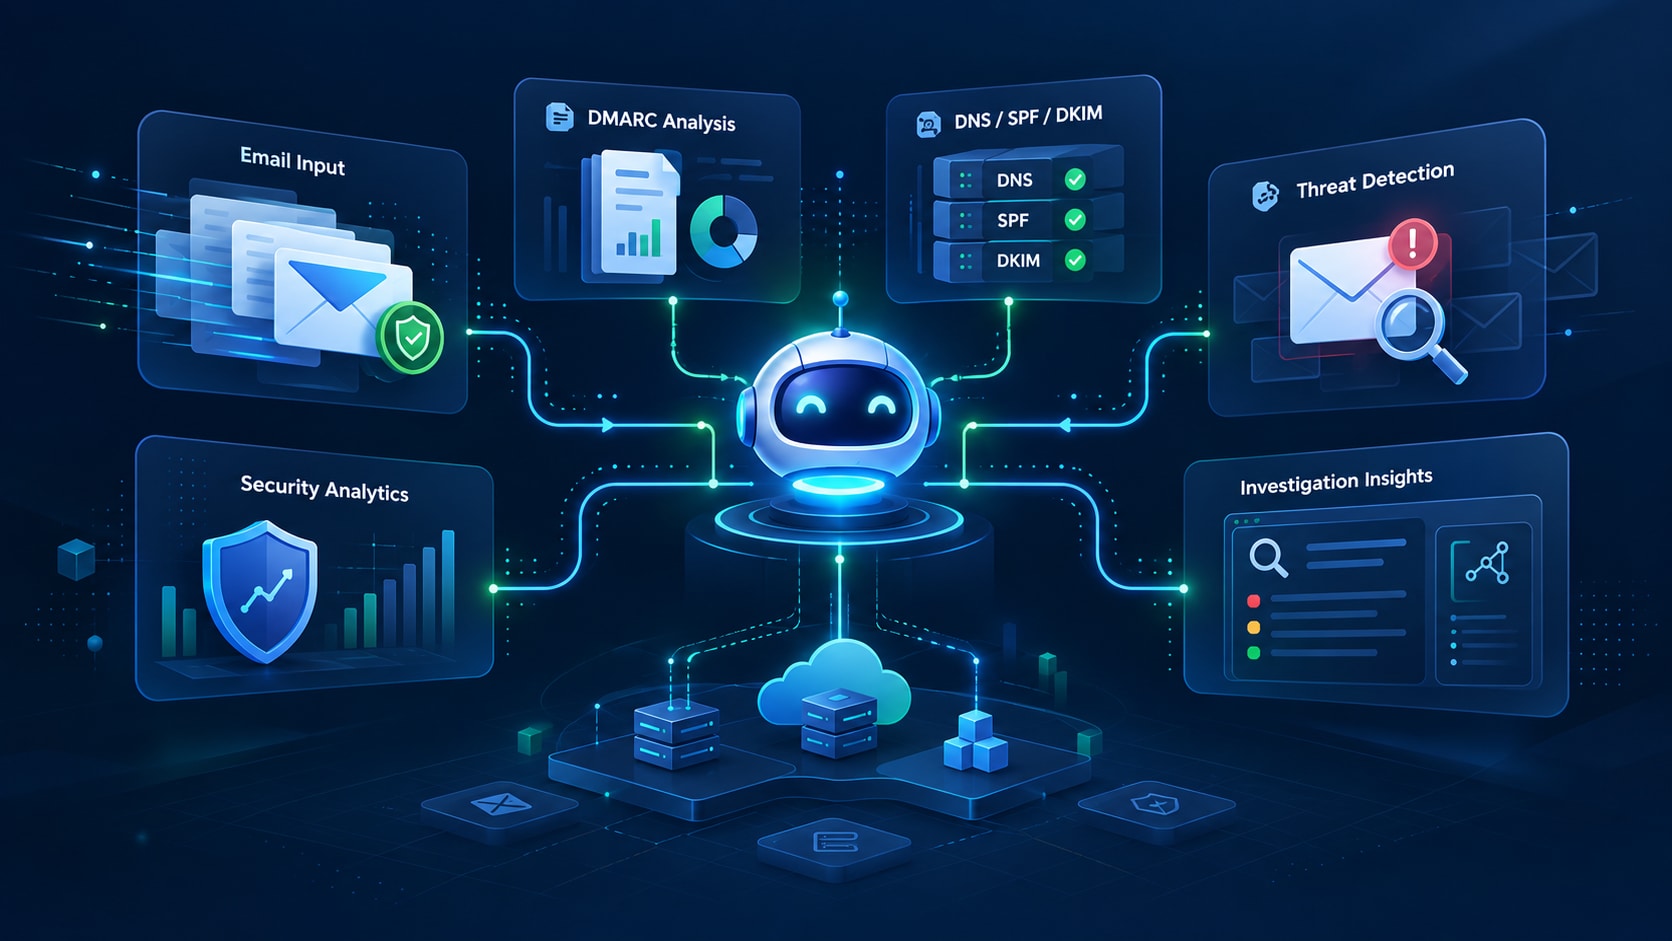
The risk, in the absence of a structured model, is having data available but not very usable: reports that are difficult to read, uncorrelated evidence, SPF/DKIM issues that are not immediately identifiable, and a lack of integration with the rest of the security sector.
EXPECTED RESULTS
Up to 30% reduction in analysis times
Thanks to agentic support in interpreting evidence, reading aggregations, and identifying recurring cases.
Up to 25% reduction in display and classification times
Thanks to aggregations by domain, subdomain, source, and type of error.
Immediate Root Cause
Reduction of the time to identify cases already attributable to the calculated Root Cause.
Low operational cost and manageable domains
Architecture designed to scale across extensive and complex perimeters, with negligible maintenance costs in ordinary scenarios, varying based on actual resource consumption
The Solution
Secure Email Agentic Manager
Our Secure Email Agentic Manager enhances DMARC data by turning it into operational insights through an Azure-based solution integrated with Microsoft Sentinel.
The platform enables the collection, correlation, and analysis of email authentication evidence, supporting security teams in monitoring, troubleshooting, and investigation activities.
DMARC Report Analysis
Analyzes DMARC reports to identify involved domains and subdomains, traffic volumes, SPF/DKIM/DMARC results, and suspicious messages.DNS Record Analysis
Quickly detects missing SPF or DKIM records, alignment issues, and misconfigurations that affect DMARC enforcement.Correlation with XDR Data
Correlates DMARC evidence with email events, phishing campaigns, compromised users, and other security signals through Microsoft Sentinel.Email Reputation Analysis
Supports the identification of unauthorized sources, unknown servers, and potential spoofing attempts, improving evidence interpretation.
How does it work? From the DMARC report to the operational response
The Secure Mail Agentic Flow allows you to transform a set of technical reports into a comprehensible, contextualized, and actionable response.
The benefits
More control over the email perimeter
The Secure Email Authentication Manager provides a more comprehensive view of the authentication status of corporate domains.
Integrate DMARC monitoring into Microsoft security processes
With the Secure Email Agentic Manager, DMARC data becomes an integral part of the corporate security posture.
The solution allows for the analysis of SPF, DKIM, and DMARC configurations, identifying errors and suspicious sources, correlating evidence with Microsoft Sentinel, and supporting operators with a dedicated intelligent agent for investigation.
We provide organizations with support in the design, implementation, and governance of Microsoft-based solutions for email perimeter protection.