
CRA conformity for connected products on AWS
The EU Cyber Resilience Act (CRA) imposes strict deadlines and penalty risks on manufacturers of connected products. We will guide you from your current architecture to a demonstrably compliant target state on Amazon Web Services (AWS), with a clear plan, proven patterns, and concrete implementation.
~90% of the CRA technical requirements covered
For manufacturers of connected products: From the current state to verifiable CRA compliance, on time for the legal deadlines.
Challenge
The CRA demands – and the clock is ticking
The Cyber Resilience Act applies to almost every connected product placed on the market in the EU. From September 11, 2026, vulnerabilities and incidents must be reported within hours, from December 11, 2027, full compliance is mandatory.
Many manufacturers are aware of the regulations but cannot translate them into concrete development work. Established processes, automated tools, and a sustainable update infrastructure over long product life cycles are lacking.
Our solution approach
Consulting and implementation in four clear phases
A practical example
Proven in industrial IoT projects
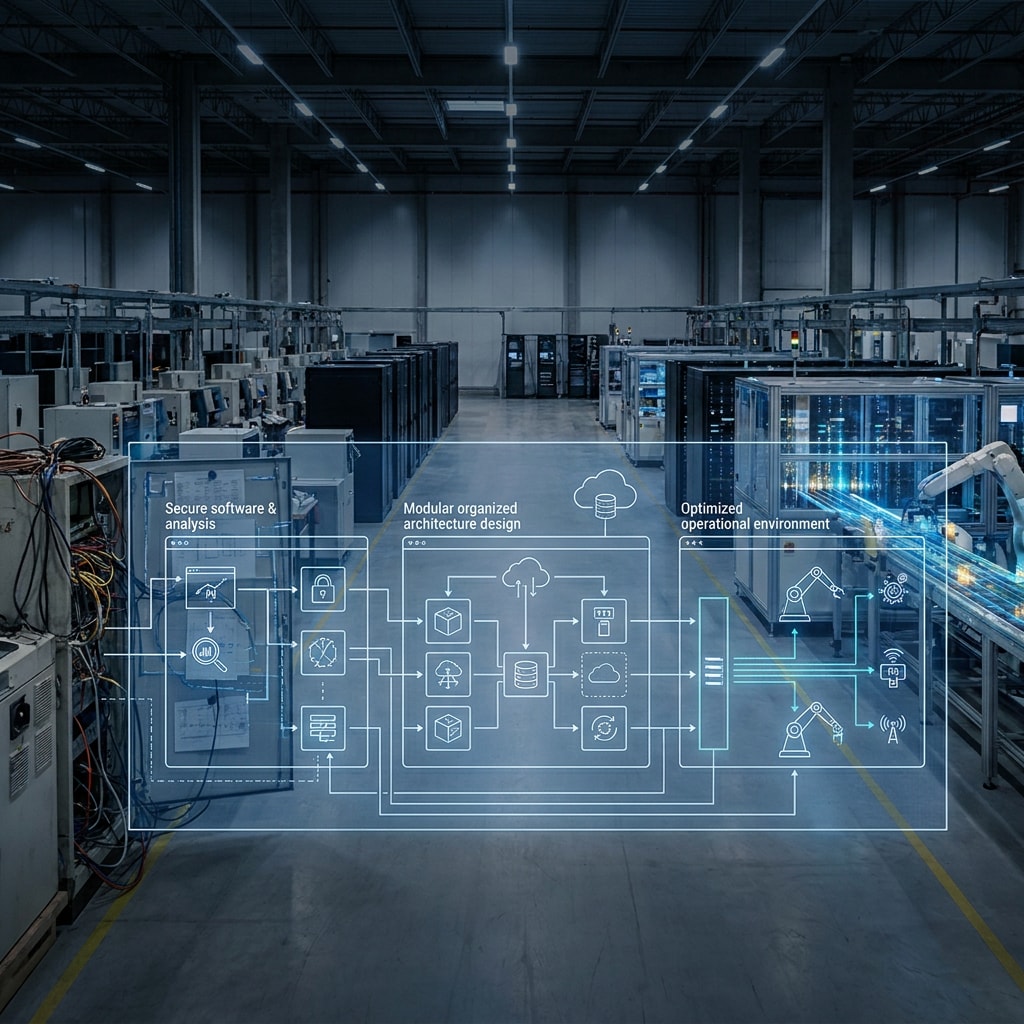
Our experience from real industrial IoT projects flows directly into the CRA implementation. For Kingspan, a global manufacturer of insulation panels, we developed a replicable "IoT in a box" based on AWS IoT SiteWise Edge. Heterogeneous control and data systems across 50 factories were unified: The application ran on AWS within a few days, processing 1.5 TB of data monthly, and the audit time per plant decreased from three weeks to three minutes. For the container terminal operator EUROGATE, we realized a TIC-4.0 data platform with Greengrass, IoT Core, and S3 for real-time capture and audit-proof CI/CD delivery. We transfer exactly these patterns, edge hardening, automated pipelines, and audit-secure documentation to CRA-specific proof pipelines.
The Technology Behind
The architecture behind conformity
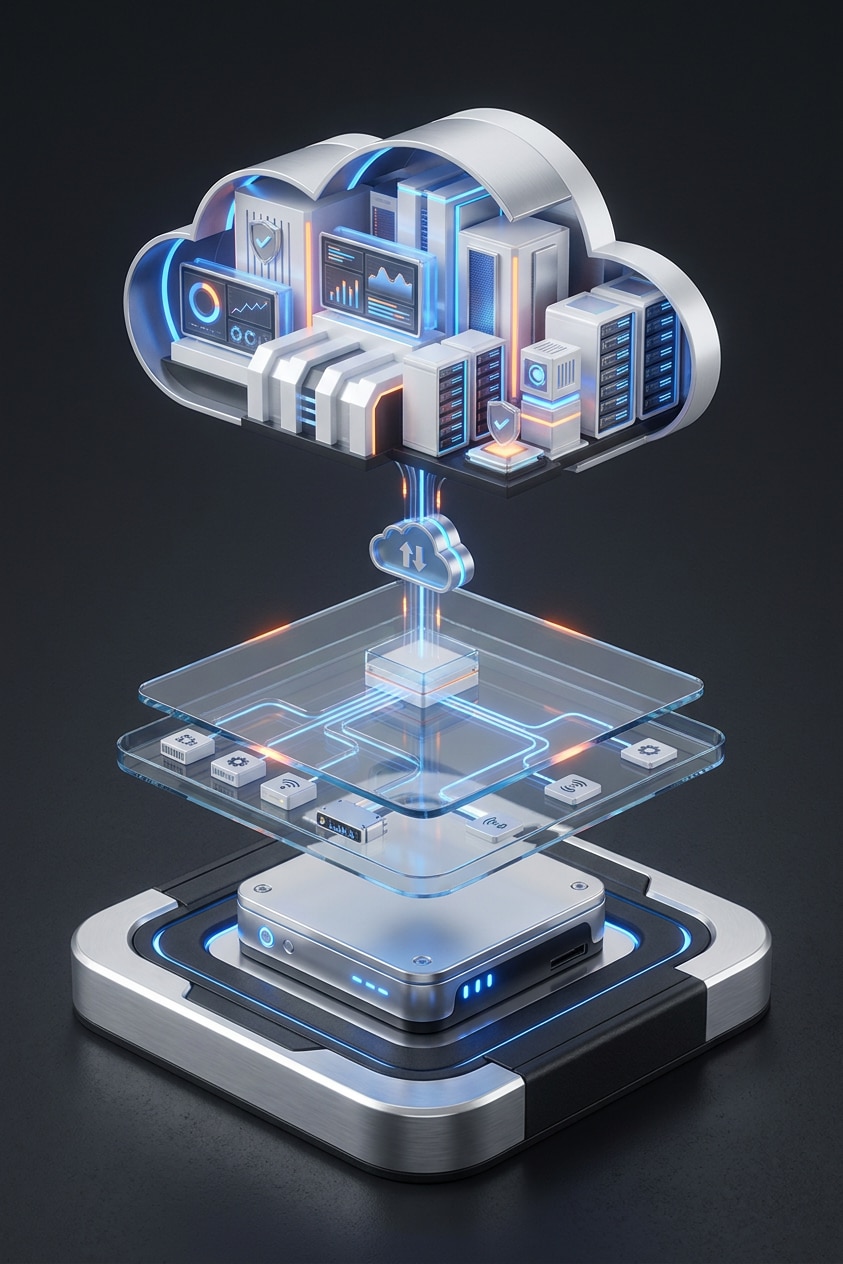
To demonstrate, we automatically generate SBOMs (Software Bill of Materials) in the CI/CD pipeline – aligned with BSI TR-03183. A PSIRT operational model covers the legal 24h/72h/14d reporting cadence via the ENISA platform. A document generator automatically creates Annex VII-compliant technical documentation from the pipeline artifacts. All data remains in European AWS regions – relevant for GDPR, NIS2, and DORA.
At its core, there is a reference architecture for a "Secure-by-Design Connected Product Platform" on AWS. On the edge side, that is, directly at the product or device, secure connectivity, signed components, and secure over-the-air updates provide protection and currency. This can be done edge-first: data remains for initial processing on-site, which reduces both bandwidth costs and the attack surface.
Benefits
Your benefits at a glance
You achieve compliance while creating a reusable foundation that alleviates future product lines and additional regulations.
Clear Compliance Path
Documented maturity for the deadline on September 11, 2026, and a clear path to full compliance by the end of 2027
90% CRA coverage
Quantified ~90% coverage of the CRA technical requirements through the AWS Well-Architected Framework Review (with IoT Lens) – remaining legal gaps are transparently identified and addressed together

Reusable architecture
Significantly lower effort per subsequent product line through reusable architectural patterns, CDK templates, and documentation generators
Ability to report demonstrated
Proven 24-hour reporting capability with automated 72-hour and 14-day cycles, integrated into the ENISA Single Reporting Platform and validated through tabletop exercises before September 2026
Automated SBOM Pipeline
Automated SBOM coverage already at build time (Syft, CycloneDX, Sigstore/Cosign), aligned with BSI TR-03183 – continuous vulnerability scanning scalable across the entire portfolio
Seamless edge cloud integration
Seamless edge cloud integration on AWS, proven in industrial production environments with IoT Greengrass, IoT SiteWise Edge, and IoT Core
Reduced fine risk
Avoiding penalty risks through documented CRA compliance by product family

Competitive advantage through compliance
Documented compliance as a competitive advantage in EU tenders
Start with a compact assessment
Do you want to know where your products stand with the CRA and what steps are necessary before the deadlines? In a 60-minute meeting, we will assess relevance together. As an AWS Premier Tier Partner and part of the Reply Group, we will guide you from the initial assessment to the pilot implementation – pragmatically and results-oriented.

Storm Reply specializes in the design and implementation of innovative cloud-based solutions and services. With extensive expertise in the creation and management of Infrastructure as a Service (IaaS), Software as a Service (SaaS), and Platform as a Service (PaaS) cloud solutions, Storm Reply supports large enterprises in Europe and worldwide in implementing cloud-based systems and applications. Storm Reply is an AWS Premier Consulting Partner.